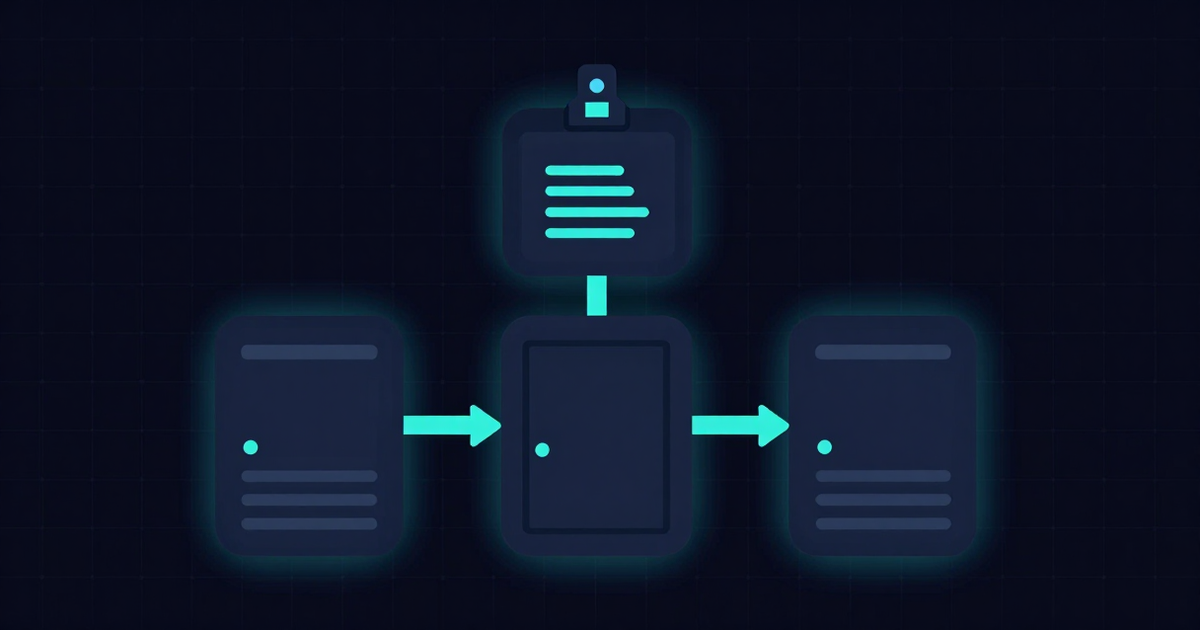
Third-Party Access Offboarding Without Breaking Services
A practical vendor offboarding checklist: identify every human and machine access path, protect dependent services, revoke access at the destination, and verify closure.
Network Failover Testing Without Surprising Users
A practical way to test primary and backup network paths: agree on critical user journeys, interruption limits, abort authority, restoration and evidence before a live change.
AI Tool Data Retention: What to Ask Before Uploading
Before staff paste business data into an AI tool, check plan-specific rules on training, chat history, access, deletion, and integrations. Use this buyer checklist to set an allowed-data rule.
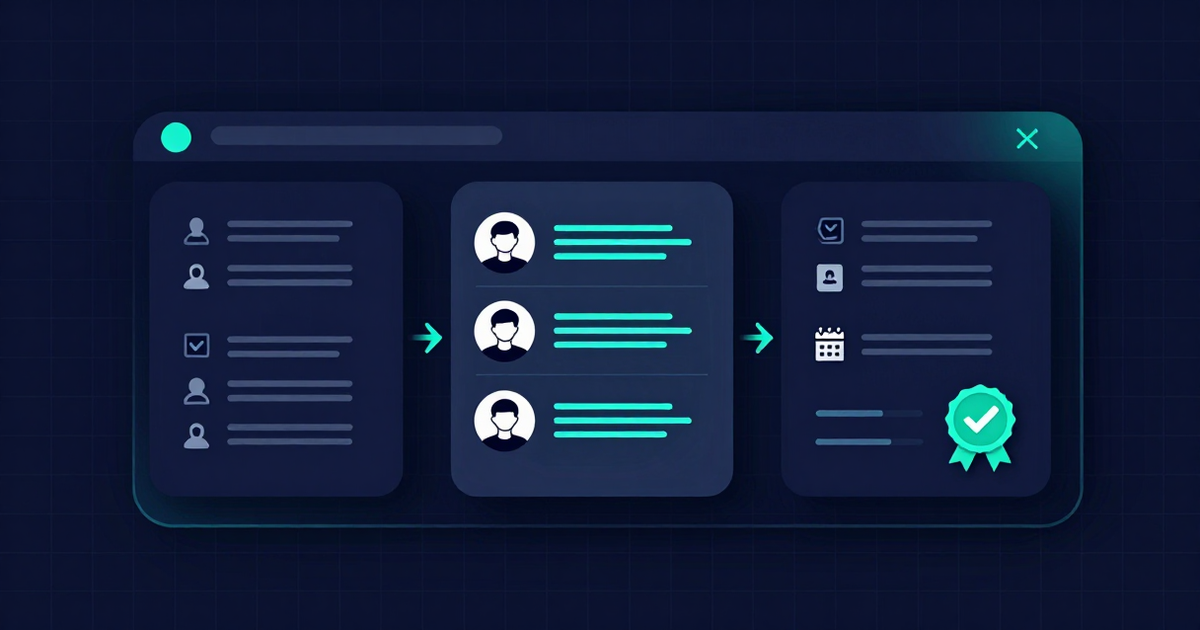
Audit Remediation Plan: From Findings to Verified Action
Turn an information security audit report into an owned action queue, prioritize findings in business context, and separate implementation from validated closure.
AhsayCBS CVE-2026-105134: Hotfix and Compromise Checks
Ahsay says earlier AhsayCBS patches did not fully fix CVE-2026-105134 and the related CVE-2026-105133. Check your branch, apply the new hotfix, and review possible exposure.
A Backup Job Ran. Can You Restore the Application?
A successful backup job is not proof that a business application will recover. Run a controlled restore test, check the application and its dependencies, and measure the results against your recovery targets.
Citrix NetScaler CVE-2026-88771 and CVE-2026-88772: Patch and Check for Compromise
Citrix NetScaler CVE-2026-88771 and CVE-2026-88772 is an actively exploited management-server flaw. Identify affected systems, restrict access, patch the correct release, and check for compromise.
Adobe Commerce CVE-2026-71362: Patch Now and Check Administrative Access
Adobe Commerce CVE-2026-71362 is an actively exploited management-server flaw. Identify affected systems, restrict access, patch the correct release, and check for compromise.
Check Point CVE-2026-93616: Patch Management Servers and Check for Compromise
Check Point CVE-2026-93616 is an actively exploited management-server flaw. Identify affected systems, restrict access, patch the correct release, and check for compromise.
Critical WordPress Vulnerability CVE-2026-87902: Update Your Website Now
CISA has confirmed exploitation of WordPress CVE-2026-87902. Site owners should install a fixed release, verify deployment, preserve logs, and check exposed systems for suspicious changes.